These setup instructions provide information for configuring SAML-based sign-in through JumpCloud for designated users in the organization to the eSHARE application. The IdP Entity ID, Service Provider Entity ID and ACS URL referenced in this document will be provided to you by eSHARE when the tenant for your organization is provisioned on the platform. The following steps will be reviewed:
PREREQUISITES:
An account with Administrator access to the JumpCloud console (https://console.jumpcloud.com).
Create the SAML Application
Log in to https://console.jumpcloud.com using the account with Administrator access and navigate to the 'SSO' menu under the 'User Authentication' section.
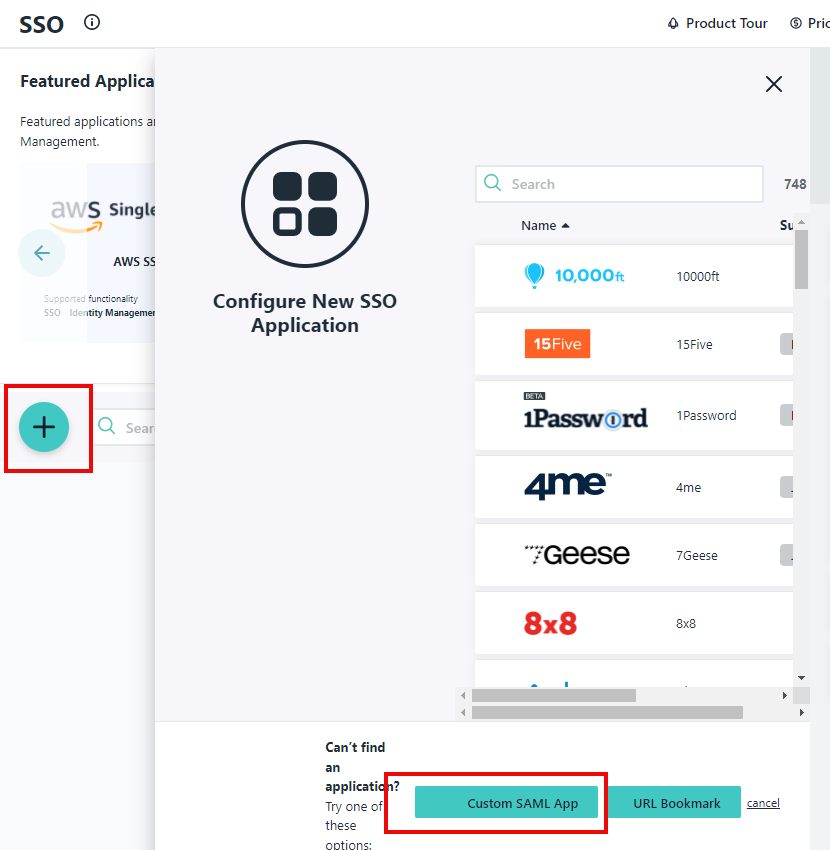
On the SSO page, click the '+' icon to add a new SSO application.
In the newly opened pane, click 'Custom SAML App'.
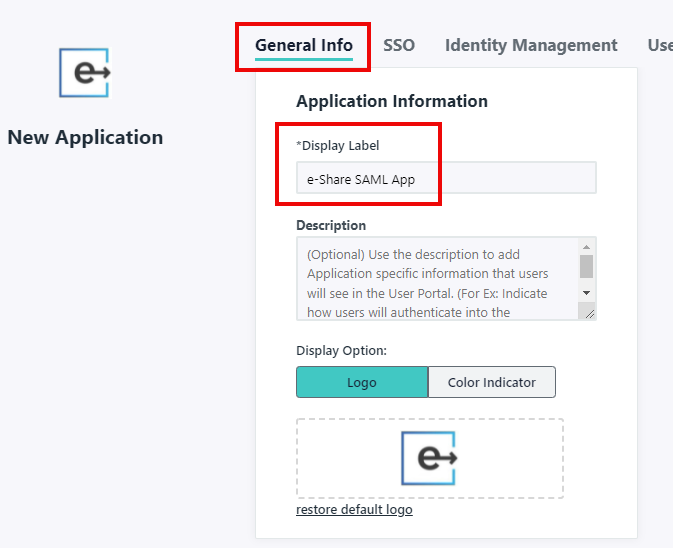
In the 'New Application' pane, under the 'General Info' tab, enter the display name and upload the eSHARE logo, if available.
Configure SAML Settings
In the same 'New Application' pane, switch to the 'SSO' tab.
Enter the 'IdP Entity ID' (st8XJRQkSguC), 'SP Entity ID' and 'ACS URL' provided by eSHARE, as shown below.
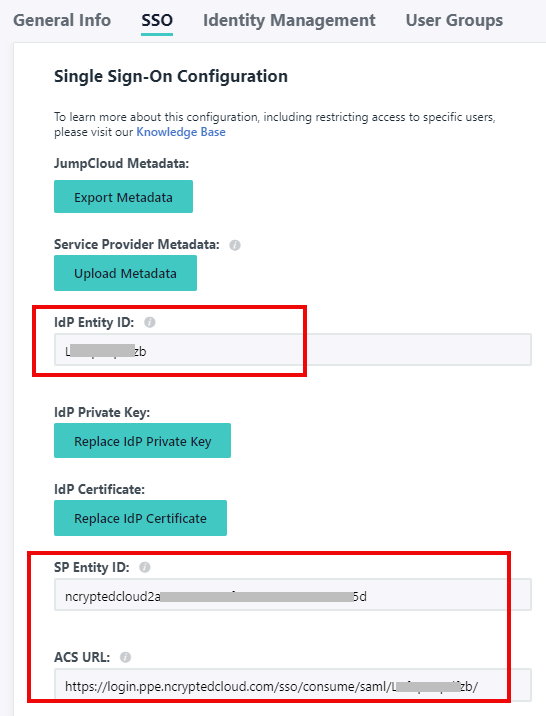
Retain 'SAMLSubjectNameID' as email and the other default values.
Map User Attributes
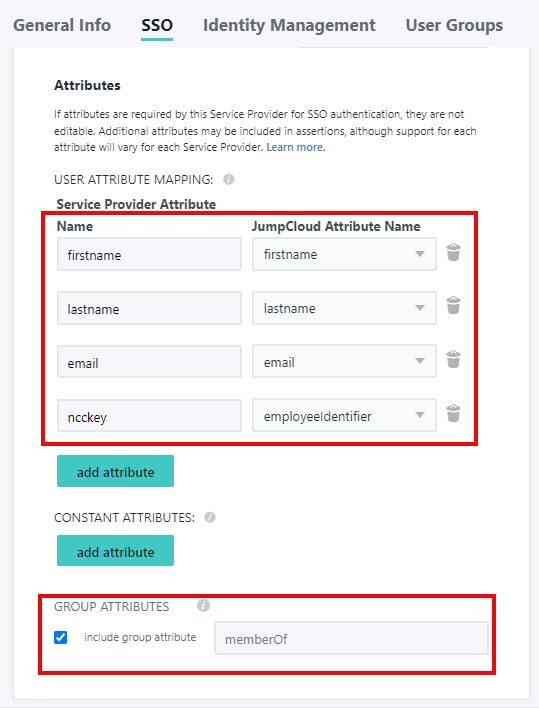
Scroll down to the 'Attributes' section.
Update the attributes as below:
firstname: mapped to the user’s first name
lastname: mapped to the user’s last name
email: mapped to the user’s email address
ncckey: mapped to any unique and immutable user attribute
Group Attributes: optional
Assign Users to the Application
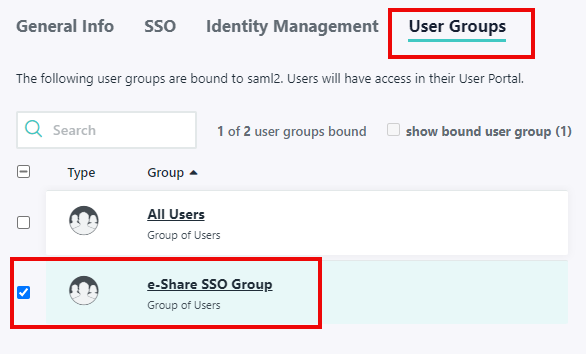
Switch to the 'User Groups' tab and select the group to which the newly created SAML application should be made available.
Scroll down to the bottom of the 'New Application' pane and click 'activate'.
Send the IdP Details to eSHARE
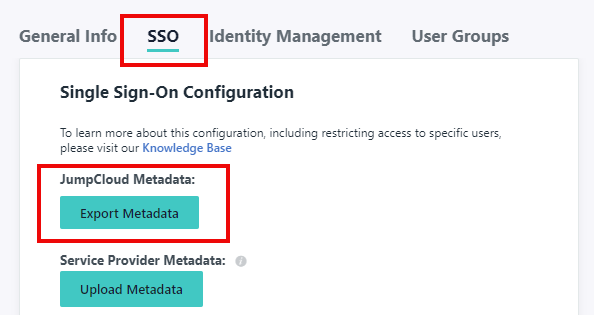
After successful activation, the new SAML application is created. Open the SAML app and switch to the 'SSO' tab.
Click the 'Export Metadata' button to export the metadata.
Send the exported metadata XML to your eSHARE Customer Success Manager.