These setup instructions provide information for configuring SAML-based sign-in through Google for all users in the organization to the eSHARE Collaborate application. The Entity ID and ACS URL referenced in this document will be provided by an eSHARE Customer Success Manager when the tenant for your organization is provisioned on the platform. The following steps will be reviewed:
Create the SAML Application
Log in to the Google Admin portal (https://admin.google.com).
Go to 'Apps' > 'SAML Apps', and click 'Add a service/App to your domain'.
On the 'Enable SSO for SAML Application' page, click the 'SETUP MY OWN CUSTOM APP' link at the bottom of the window.
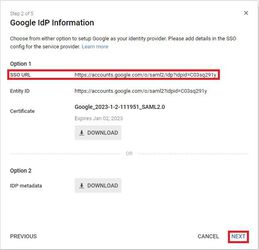
On the 'Google IdP information' page, copy the 'SSO URL' to provide back to the eSHARE Customer Success Manager.
Select 'NEXT'.
On the 'Basic information for your Custom App' screen, for 'Application Name', enter eShare. Upload the eSHARE logo, if provided, and click 'NEXT'.
Configure SAML Settings
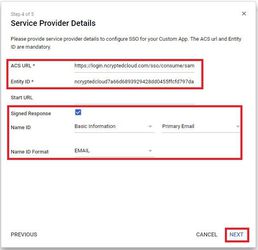
On the 'Service Provider Details' page, fill in the details using the information provided by eSHARE, as shown below:
'ACS URL' (provided by Customer Success)
'Entity ID' (provided by Customer Success)
'Signed Response': Enabled
'Name ID': Basic Information; Primary Email
'Name ID Format': Email
Map User Attributes
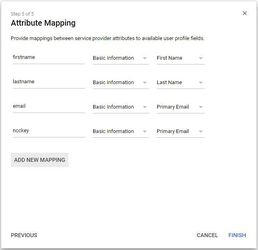
On the 'Attribute Mapping' screen, click 'ADD NEW MAPPING' to add the following attributes:
firstname: Basic Information, First Name
lastname: Basic Information, Last Name
email: Basic Information, Primary Email
ncckey: Basic Information, Primary Email
When done, click 'FINISH'.
Assign Users to the Application
Go back to 'Apps' > 'SAML Apps' and verify that the 'Status' for the eShare application shows 'ON for everyone'.
If it does not, click the menu option at the far right and select 'On for everyone'.
Send the IdP Details to eSHARE
Click the eShare application link and, on the 'Settings for eShare' page, click the 'Service Provider Details' section.
Click the 'Manage Certificates' link under the 'Certificates' information.
On the 'Manage identity provider certificates' screen, click the 'DOWNLOAD CERTIFICATE' link to save the certificate.
Send the following to eSHARE to complete the SAML SSO setup process:
SSO URL (copied in step 4 of Create the SAML Application)
Certificate (saved in step 3 above)