Previously, a single Sharing Policy in your tenant could be assigned the 'Access Link' module, and every Access Link / External Link share inherited that one policy's permissions, login, collaboration, and approval settings. That dedicated module was retired on November 4, 2026. This article explains how Sharing Policy and Link auto-approval now work for External Link, and how to configure them. The following sections are covered:
What's Changed
The dedicated Access Link Sharing Policy module is retired — you no longer assign a policy specifically to 'Access Link'.
Every External Link now resolves its Sharing Policy the same way a regular Trusted Share does: a sensitivity label, an explicit site assignment, or a DLP tag determines (and locks) the policy; otherwise a default policy applies.
The 'Link auto-approval' setting that used to live only in the dedicated Access Link policy is now available on every Sharing Policy — configure it on whichever policy applies to your External Links.
For the full picture on this release, see 'What's Changing with External Link (formerly Access Link)'.
Note:
Existing Access Link shares created under the old dedicated policy are not affected — they continue to work with the settings they were created under. This change applies only to new External Links created after the update.
How eShare Determines the Sharing Policy for External Link
The Sharing Policy applied to an External Link follows the same precedence used for a regular Trusted Share:
Sensitivity label (if the item, SharePoint site, or OneDrive has a sensitivity label applied) — the mapped policy is shown and locked.
Explicit policy assignment (if a policy has been directly assigned to the site) — that policy is shown and locked.
DLP tag (if the item has a DLP rule triggered and a tag is created with the rule) — the mapped policy is shown and locked.
Default policy (if none of the above applies) — the default Sharing Policy is used.
Configure Link Auto-Approval on a Sharing Policy
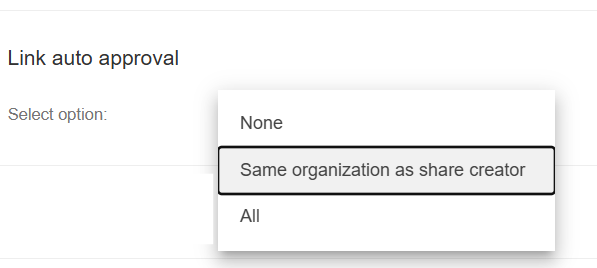
The Link auto-approval setting controls whether the share owner must approve someone before they can access an External Link they weren't named on. Since this is now set per policy rather than in one dedicated policy, review it on each Sharing Policy that applies to your External Links.
PREREQUISITES:
Admin access to the eSHARE Admin Console
Navigate to 'Admin Console' > 'Sharing Policies'.
Open the Sharing Policy that applies to your External Links — the one mapped to the relevant sensitivity label or site assignment, or your organization's default policy.
Find the 'Link auto-approval' setting.
Choose the option that matches your workflow:
Setting | Behavior | Use when |
|---|---|---|
None | The owner reviews and approves each recipient after the link is opened. | You want visibility into who is accessing the share before granting access. |
Same Organization as Share Creator | Recipients in the creator's organization access the share without owner approval. External recipients still require approval. | Internal recipients should have seamless access; external recipients should be gated. |
All | All intended recipients access the share without owner approval. | Recipients are pre-vetted and no per-recipient approval step is needed. |
Save the policy.
Notes
Changing the Link auto-approval setting affects new links created after the change. Existing links continue to follow the setting that was in effect when they were created.
How the Old Access Link Sharing Policy Worked
PREREQUISITES:
Admin access to the eSHARE Admin Console
An existing Sharing Policy that can be duplicated as a starting point
Confirmation that no other Sharing Policy in your tenant is already assigned the Access Link module (only one policy can hold this assignment)
Create the Access Link Sharing Policy
Navigate to 'Admin Console' > 'Sharing Policies', locate a Sharing Policy that most closely matches the configuration you want for Access Link shares and duplicate it.
Rename the copy to clearly identify its purpose (for example, Access Link Policy).
Open the duplicated policy and navigate to 'Sharing Modules Assignment'.
Assign 'Access Link' only. Do not assign OneDrive or SharePoint to this policy.
Note:
The Access Link module can be assigned to only one Sharing Policy at a time. If it is already assigned elsewhere, you must remove it from that policy first.

Within the policy, configure the remaining options as required for your Access Link shares, including:
'Permissions' — what recipients can do with the share
'Login' — whether recipients must authenticate before accessing the share
'Collaboration' — co-authoring and related settings
Choose an Access Link Auto-Approval Setting
The auto-approval setting controls whether the share owner must approve recipients before they can access the share. Choose one of the following based on your workflow:
Setting | Behavior | Use when |
|---|---|---|
None | The owner reviews and approves each recipient after the link is created. | You want visibility into who is accessing the share before granting access. |
Same Organization as Share Creator | Recipients in the creator's organization access the share without owner approval. External recipients still require approval. | Internal recipients should have seamless access; external recipients should be gated. |
All | All intended recipients access the share without owner approval. | Recipients are pre-vetted and no per-recipient approval step is needed. |

Save and Validate the Policy
Save the policy.
Create a test Access Link Trusted Share and confirm that the permissions, login, collaboration, and auto-approval behaviors match expectations.
Notes
Only one Sharing Policy in the tenant can have the Access Link module assigned. Plan accordingly if you maintain multiple environments or use cases.
Changing the auto-approval setting affects new shares created after the change. Existing shares continue to follow the policy as it was configured when they were created (verify this against your platform behavior before publishing).