This document outlines the steps a new customer needs to take when installing the eSHARE Collaborate product. It also provides the required administrator roles and resources needed to complete the installation. The following sections are covered:
MySQL or Azure SQL Database for Secure Conversations (Core Product & Secure Mail Module)
Azure Storage Account for Inline Images (Core Product & Secure Mail Module)
Native eSHARE M365 Trusted Sharing Action Menu App (Core Product)
DNS Entries (Core Product)
PREREQUISITES:
An administrator who has access and can manage the DNS entries of the company domain.
How to Install: DNS Entries will be provided by your eSHARE Customer Success Manager.
What is Required: DNS entries will need to be entered for the Company Domain.
Why is this needed: They are required for the following reasons:
A CNAME entry is required for the eSHARE Web Portal where users can manage their Trusted Shares, e.g. secure.DOMAIN.com.
A CNAME entry is required for the ShareWithMe Link, e.g. sendto.DOMAIN.com.
2 SPF TXT records are required for Branded email notifications and delivery.
An optional CNAME entry for email tracking.
DMARC – update to include records for email notifications.
DKIM – update to include records for email notifications.
Single Sign-On Integration: SAML2 (Core Product)
PREREQUISITES:
An administrator with the M365 Global Administrator Role or Application Administrator Role.
How to Install: Single Sign-On (SSO) Configuration
What is Required: Administrator will create an eSHARE SAML Application in Azure Active Directory Enterprise Applications using instructions provided by the eSHARE Customer Success Team.
Why is this needed: Creating a Single Sign-On Application will allow users to seamlessly log in to the eSHARE Web Portal using the organization’s IdP provider and removes the need to create a separate username and password. It is more secure and allows administrators to manage a single identity.
Aside from Microsoft Entra ID, eSHARE also integrates seamlessly with Single Sign-On (SSO) solutions leveraging federated identity providers (IdPs) such as Okta, PingID, and other standards-based providers.
App Registration in Microsoft Entra ID (Core Product)
PREREQUISITES:
An administrator with the M365 Global Administrator Role, and an eSHARE Administrator.
How to Install: Create eShare Entra ID App Registration
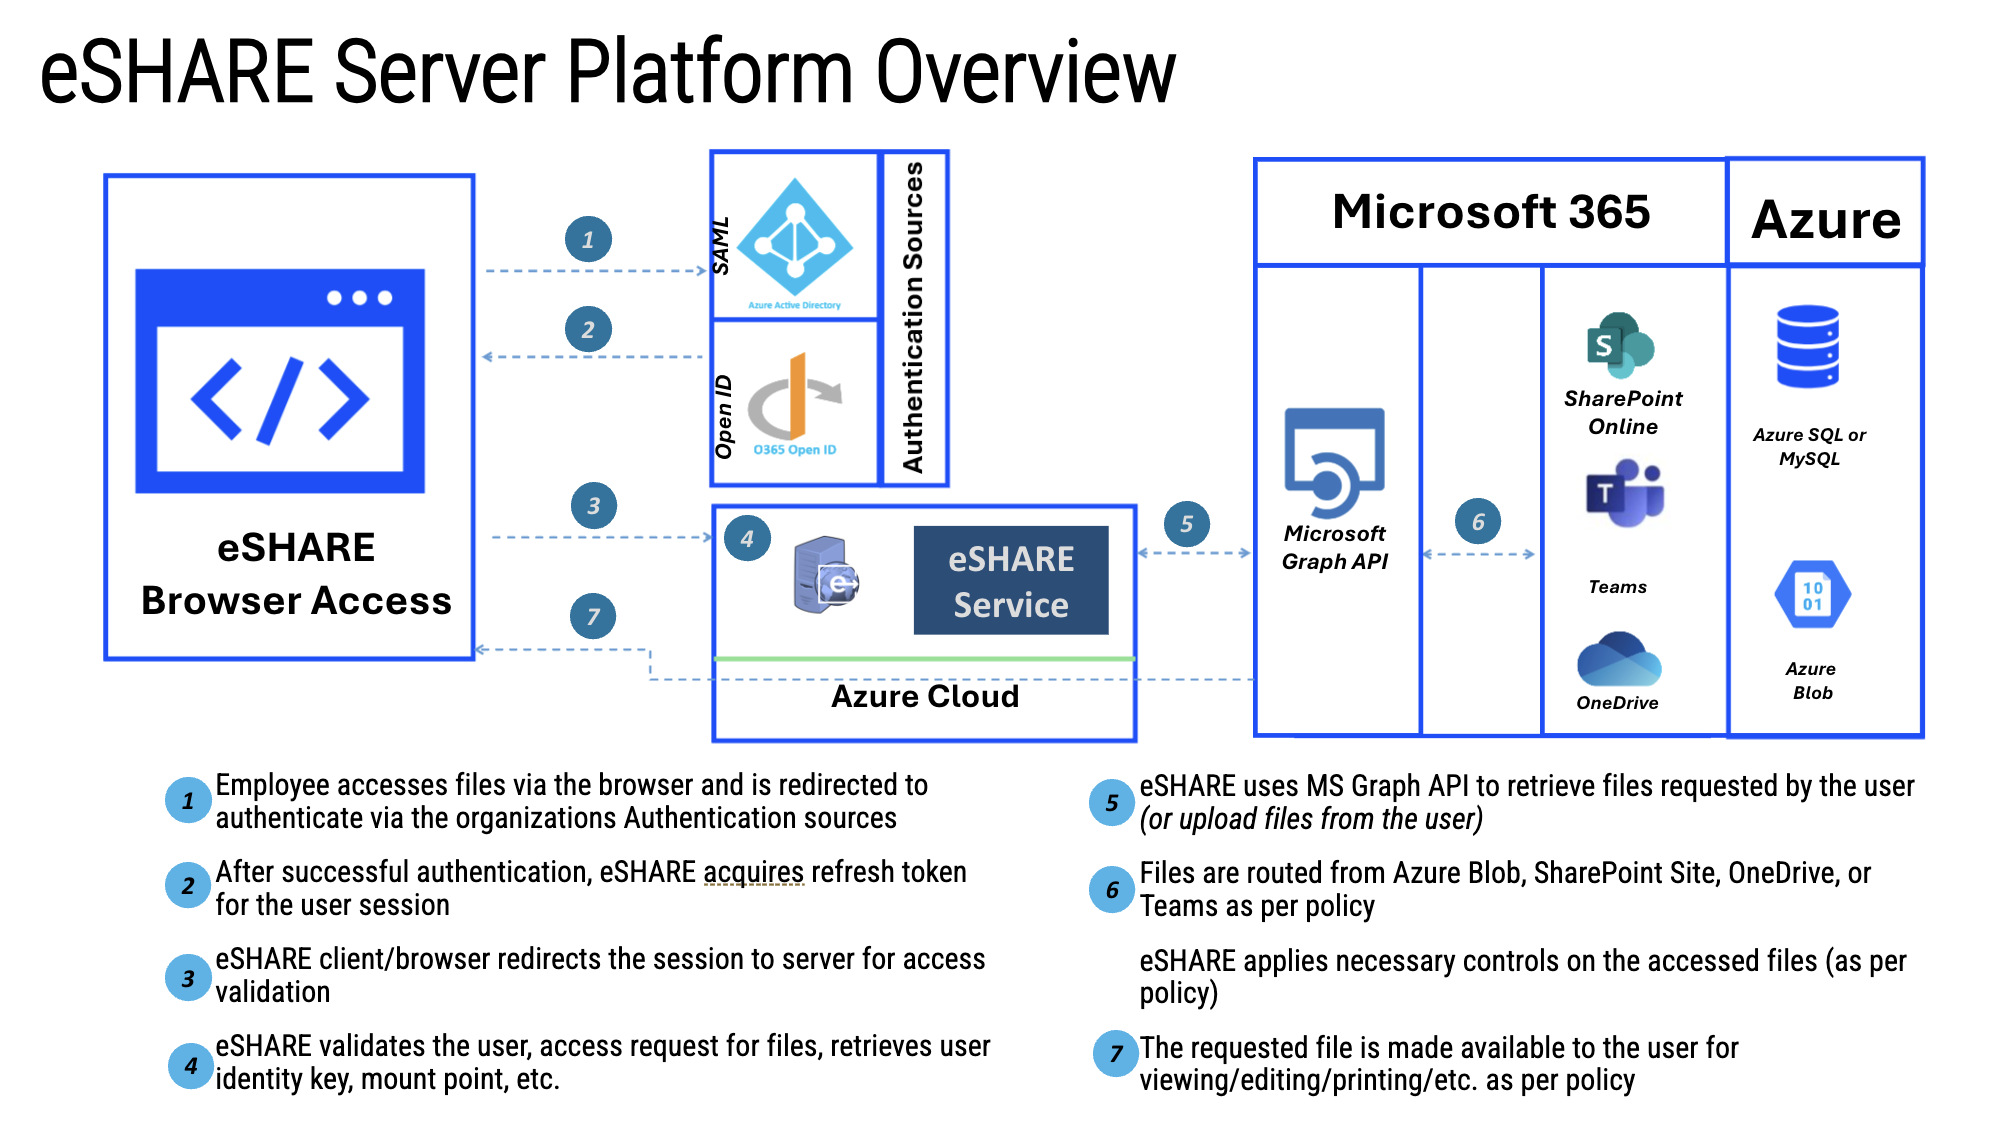
What is Required: M365 Administrator will create an App Registration in Entra ID, providing the App specific API permissions which allows eSHARE to integrate with OneDrive, SharePoint, Teams, and Sensitivity labels. A Certificate and Private Key pair is also needed for the eSHARE Application to authenticate with the created Service Principal.
Why is this needed: Creating the eSHARE app registration and consenting to specific GRAPH API permissions (see below for specifics on API Permissions) creates the eSHARE Service Principal in the Organization’s M365 Enterprise Application, and provides access to the Cloud Providers (OneDrive, SharePoint, and Teams). This will allow users in your organization to Share Data in their OneDrive, SharePoint, and Teams through the eSHARE application. Additionally, it creates a link to the organizations defined Sensitivity Labels, allowing the ability to map the labels to Sharing policies enabling active controls when sharing sensitive data.
MySQL or Azure SQL Database for Secure Conversations (Core Product & Secure Mail Module)
PREREQUISITES:
An administrator with Azure Subscription Owner Role or Contributor Role, and an eSHARE Administrator.
How to Install: MySQL Database for Secure Messages or Azure SQL Database for Secure Messages
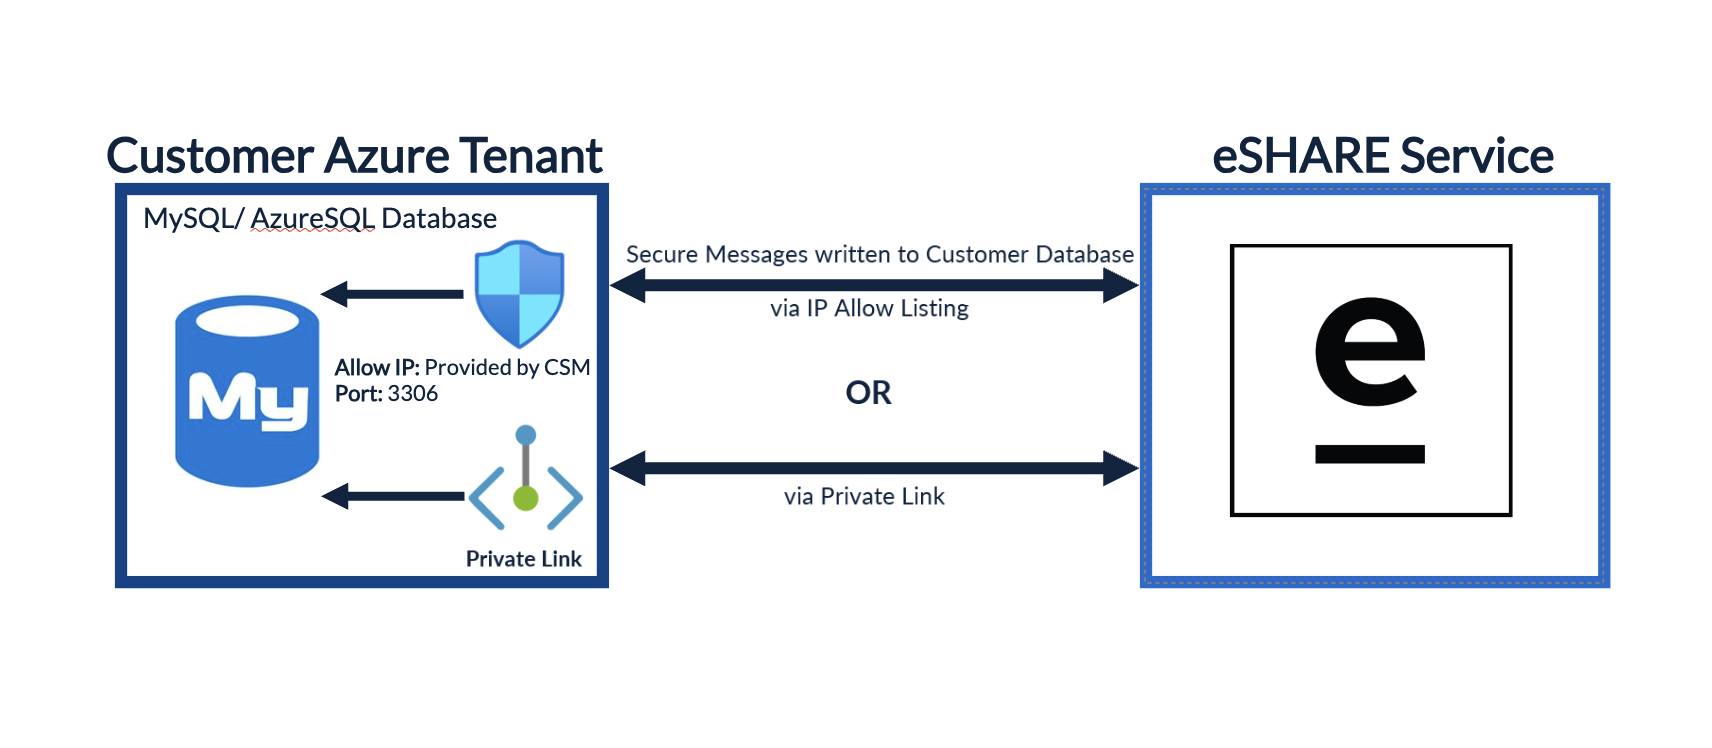
What is Required: Administrator will create a MySQL or Azure SQL database in Azure that will store the text from secure conversations. The eSHARE admin will then enter the database information into the eSHARE Admin Console to complete the connection.
Why is this needed: Creating the MySQL or Azure SQL Database allows the organization to store all Secure Conversations that occur in Trusted Shares within their own environment. This allows the organization to store their own data in their environment instead of storing it in eSHARE’s database.
Azure Storage Account for Inline Images (Core Product & Secure Mail Module)
PREREQUISITES:
An administrator with Azure Subscription Owner Role or Contributor Role, and an eSHARE Administrator.
How to Install: Adding Azure Blob Storage Account for Images
What is Required: Administrator will create an Azure Blob Storage Account that will store inline images that are sent through a secured email or within secure conversations. The eSHARE admin will then enter the storage information into the eSHARE Admin Console to complete the connection.
Why is this needed: Creating the Azure Blob Storage Account allows the organization to store/host all inline images that are sent through a secured email or through secure conversations within their own environment. If there is no storage account linked to the organization’s eSHARE tenant, inline images will not be uploaded into the secure conversations.
Native eSHARE Trusted Sharing M365 App (Core Product)
PREREQUISITES:
An administrator with M365 Global Administrator Role or SharePoint & Teams Administrator Role.
How to Install: M365 Application Installation Guide
What is Required: Administrator will install the eSHARE Trusted Sharing application from the M365 SharePoint store and will provide consent to the needed Graph API Access within SharePoint Admin page.
Why is this needed: The eSHARE Trusted Sharing Application allows users within the organization to create and manage Trusted Shares natively within Teams, SharePoint, Outlook, and the Office Homepage. It creates a better user experience by removing the need to use the eSHARE Web Portal to share files and removes the burden of needing to register Teams/SharePoint Sites in the eSHARE Admin Console.
Native eSHARE M365 Trusted Sharing Action Menu App (Core Product)
Note:
If installed, the app will appear org-wide within OneDrive, SharePoint, and Teams. It can be considered optional, but it is still recommended to install.
PREREQUISITES:
An administrator with Global Administrator Role.
How to Install: External Share Action Menu App Installation Guide
What is Required: Administrator will install the eSHARE Action Menu app as an Enterprise Application and will provide consent to the needed Graph API Access.
Why is this needed: The M365 Trusted Sharing Action Menu allows users to create Trusted Shares from the action menus that M365 presents to users when a file or folder is selected from within Teams, SharePoint Online, and OneDrive. Users enjoy all the benefits of external file sharing using eSHARE while never leaving M365. This greatly improves user productivity and dramatically reduces the need for change management and training.
Exchange Mail Connectors (Secure Mail Module)
PREREQUISITES:
An administrator with M365 Global Administrator Role or Exchange Administrator Role.
How to Install: Install Secure Collaboration Gateway
What is Required: Administrator will create an Inbound Connector and an Outbound Connector that will route mail to the eSHARE Secure Mail Gateway.
Why is this needed: To utilize the Secure Mail Gateway feature, these connectors must be created so outgoing mail is routed to the SMG Appliance and can be properly secured based on the classification the email was given. The Appliance will also need to send confirmation or bounce emails for any outgoing mail that was sent.
Client Infrastructure - Customer Specific
In some cases an organization may have network appliances (CASB, IDS, Firewall, proxy, etc.) that may block access to eSHARE service URLs. Ensure that the following URLs are on the organization’s allow list.
For Commercial tenants:
*.n11d.com
email.DOMAIN.com (subdomain may be different)
secure.DOMAIN.com (subdomain may be different)
sendto.DOMAIN.com (subdomain may be different)
For Government tenants:
email.DOMAIN.com (subdomain may be different)
secure.DOMAIN.com (subdomain may be different)
sendto.DOMAIN.com (subdomain may be different)
Required API Permissions
eSHARE Solution | eSHARE feature | API category | API permission | Type | Granted through | Description | What eSHARE uses it for |
|---|---|---|---|---|---|---|---|
eSHARE Collaborate | Microsoft Sensitivity Labels | Azure Rights Management Services | Content.DelegatedReader | Application | Admin consent | Read protected content on behalf of a user. | Required to access content protected by sensitivity labels, so labeled files can continue to be shared securely using label-based Sharing Policies. |
eSHARE Collaborate | Microsoft Sensitivity Labels | Azure Rights Management Services | user_impersonation | Delegated | User consent | Use Azure Rights Management to access protected content as the signed-in user. | Required to access content protected by sensitivity labels, so labeled files can continue to be shared securely using label-based Sharing Policies. |
eSHARE Collaborate | Microsoft Sensitivity Labels | Microsoft Information Protection Sync Service | UnifiedPolicy.Tenant.Read | Application | Admin consent | Read all unified policies (labels and label policies) of your tenant. | Syncs your sensitivity labels so labeled content can continue to be shared securely using label-based Sharing Policies. |
eSHARE Collaborate | Microsoft Sensitivity Labels | Microsoft Information Protection Sync Service | UnifiedPolicy.User.Read | Delegated | User consent | Read all unified policies a user has access to. | Syncs your sensitivity labels so labeled content can continue to be shared securely using label-based Sharing Policies. |
eSHARE Collaborate | OneDrive/SharePoint | Microsoft Graph | Directory.Read.All | Application | Admin consent | Read directory data such as users, groups and apps. | Looks up users and groups in your directory when sharing and managing recipients. |
eSHARE Collaborate | OneDrive/SharePoint | Microsoft Graph | Files.ReadWrite.All | Application | Admin consent | Read, create, update and delete files in all site collections without a signed-in user. | Lets eSHARE give recipients access to files shared from OneDrive, SharePoint and Teams, and apply share actions such as uploads. |
eSHARE Collaborate | OneDrive/SharePoint | Microsoft Graph | Group.Read.All | Application | Admin consent | List groups and read their properties and memberships. | Reads Microsoft 365 groups and Teams so shares can be created from them. |
eSHARE Collaborate | OneDrive/SharePoint | Microsoft Graph | GroupMember.Read.All | Application | Admin consent | Read group properties and memberships. | Reads group membership so owners and members can be included in shares. |
eSHARE Collaborate | OneDrive/SharePoint | Microsoft Graph | Sites.ReadWrite.All | Application | Admin consent | Create, read, update and delete documents and list items in all site collections without a signed-in user. | Lets eSHARE give recipients access to content shared from SharePoint sites and libraries. |
eSHARE Collaborate | User Identity | Microsoft Graph | User.Read.All | Application | Admin consent | Read user profiles in your organization without a signed-in user. | Identifies your users so they can create and manage Trusted Shares. |
eSHARE Collaborate | Shared Mailbox & Microsoft Purview DLP | Office 365 Exchange Online | Exchange.ManageAsApp | Application | Admin consent | Access Exchange Online as the application, without a signed-in user. | Powers Secure Mail (Secure Collaboration Gateway), including sending secure mail from shared mailboxes. |
eSHARE Collaborate | Microsoft Purview DLP | Office 365 Management APIs | ActivityFeed.Read | Application | Admin consent | Read activity data for your organization. | Required to read and keep up to date with DLP activity and events from Microsoft Purview, so your DLP policies can be applied to eSHARE shares. |
eSHARE Collaborate | Microsoft Purview DLP | Office 365 Management APIs | ActivityFeed.ReadDlp | Application | Admin consent | Read DLP policy events, including detected sensitive data. | Required to read and keep up to date with DLP activity and events from Microsoft Purview, so your DLP policies can be applied to eSHARE shares. |
eSHARE Collaborate | SharePoint Search & Microsoft Sensitivity Labels | SharePoint | Sites.Read.All | Application | Admin consent | Read documents and list items in all site collections without a signed-in user. | Enables search across SharePoint content and reading the sensitivity labels applied to files. |